Testpassport

 sales@testpassport.jp

下記はCompTIA CAS-003試験問題集は実際の試験問題のバージョンの一部です。 CompTIA CASP+ CAS-003問題集 は実際の試験問題バージョンには683問になります。すべての実際の試験問題は、勉強者が最初の試みで成功することを保証できます。CAS-003問題集の実際の試験問題でCompTIA試験に不合格になった場合、全額で支払い手数料の払い戻しを受けられます。実際の試験問題をトレーニングしたいでしょうか? では、トレーニングしましょう!

 CAS-003フルバージョンを入手

問題#1

A security analyst is reviewing the corporate MDM settings and notices some disabled settings, which consequently permit users to download programs from untrusted developers and manually install them. After some conversations, it is confirmed that these settings were disabled to support the internal development of mobile applications. The security analyst is now recommending that developers and testers have a separate device profile allowing this, and that the rest of the organization’s users do not have the ability to manually download and install untrusted applications.
Which of the following settings should be toggled to achieve the goal? (Choose two.)

A. OTA updates
B. Remote wiping
C. Side loading
D. Sandboxing
E. Containerization
F. Signed applications

問題#2

An engineer is evaluating the control profile to assign to a system containing PII, financial, and proprietary data.
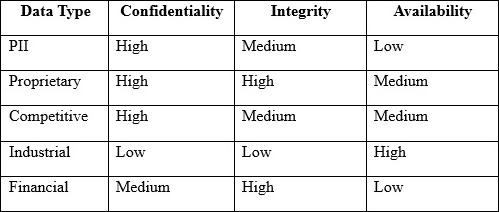


Based on the data classification table above, which of the following BEST describes the overall classification?

A. High confidentiality, high availability
B. High confidentiality, medium availability
C. Low availability, low confidentiality
D. High integrity, low availability

問題#3

To prepare for an upcoming audit, the Chief Information Security Officer (CISO) asks for all 1200 vulnerabilities on production servers to be remediated. The security engineer must determine which vulnerabilities represent real threats that can be exploited so resources can be prioritized to migrate the most dangerous risks. The CISO wants the security engineer to act in the same manner as would an external threat, while using vulnerability scan results to prioritize any actions.
Which of the following approaches is described?

A. Blue team
B. Red team
C. Black box
D. White team

Explanation:
Reference: http://resources.infosecinstitute.com/the-types-of-penetration-testing/#gref

問題#4

A recent penetration test identified that a web server has a major vulnerability. The web server hosts a critical shipping application for the company and requires 99.99% availability. Attempts to fix the vulnerability would likely break the application. The shipping application is due to be replaced in the next three months.
Which of the following would BEST secure the web server until the replacement web server is ready?

A. Patch management
B. Antivirus
C. Application firewall
D. Spam filters
E. HIDS

問題#5

An organization has employed the services of an auditing firm to perform a gap assessment in preparation for an upcoming audit. As part of the gap assessment, the auditor supporting the assessment recommends the organization engage with other industry partners to share information about emerging attacks to organizations in the industry in which the organization functions.
Which of the following types of information could be drawn from such participation?

A. Threat modeling
B. Risk assessment
C. Vulnerability data
D. Threat intelligence
E. Risk metrics
F. Exploit frameworks

試験コード: CAS-003問題数量: 683 Q&As更新時間:  2022-04-12

  CAS-003フルバージョンを入手